Most technology newsletters tell you what to buy. This one tells you what to watch for.
IN THIS ISSUE
- · The Devices Nobody Owns
- · Two years running on CRN's Solution Provider 500
- · What to watch: the gap between confident and covered
FEATURE
The Devices Nobody Owns
Two federal advisories landed eight days apart this month. The first warned that state-sponsored actors are working through poorly configured network devices across communications, energy, financial services, government, and healthcare. The second updated earlier guidance on attackers targeting the programmable controllers that run physical equipment, and it widened the list of affected manufacturers.
Read together, they are not really a story about new attack techniques. They are a story about ownership. The equipment getting picked off tends to sit in a seam: the router that came with the building, the controller the facilities team inherited, the switch installed by a vendor who is no longer under contract. Nobody chose it, so nobody patches it.
That gap is fixable, and the work is unglamorous:
- Inventory what is actually connected, not what the diagram says. Diagrams age faster than equipment.
- Assign an owner by name, not by team. "The network team" is not an owner.
- Deal with default and shared credentials on gear that predates your current staff.
- Keep the equipment that runs physical things on its own segment, away from the general network.
- Watch for quiet changes. The recent guidance specifically flagged modified code inside reusable modules on industrial controllers, the kind of change that does not announce itself.
- Put third-party access on the same map. A vendor's connection into your environment is your exposure, whether or not you set it up.
None of this needs new budget. It needs someone to decide who is responsible, before circumstances decide for you.
So here is the question worth sitting with: if an advisory dropped tomorrow naming a device class in your environment, how long would it take you to find out whether you have any?
COMPANY NEWS
Two years running on CRN's Solution Provider 500
A short piece of company news. Zinfinity has been named to the 2026 CRN® Solution Provider 500, our second consecutive year on the list. CRN, a brand of The Channel Company, publishes the ranking each year to recognize North America's largest solution providers by revenue, and it puts a channel spotlight on some of the industry's most successful companies.
We will say much the same thing we said last time, because it still holds. Revenue measures scale, and scale is genuinely useful to customers: it means the reach and the structure are there when a project crosses regions or systems. What a revenue ranking cannot measure is whether anyone is still engaged after the purchase order clears. That part is on us, every year, list or no list. Thanks to the customers and partners who keep us here.
WHAT TO WATCH
The gap between confident and covered
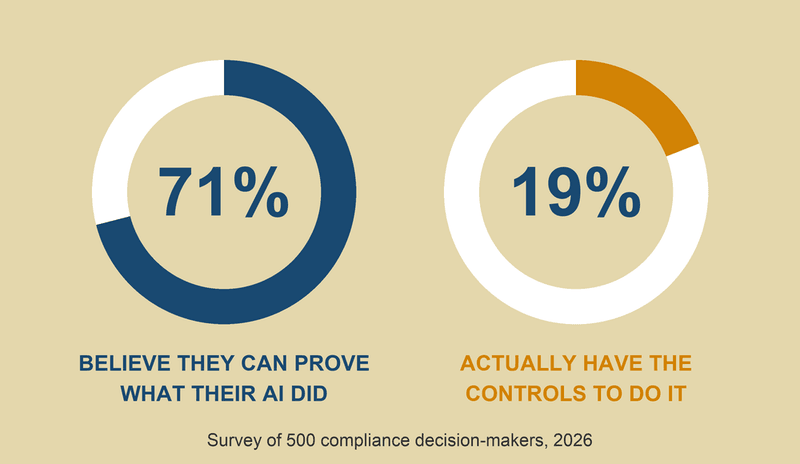
A survey of 500 compliance decision-makers published this month found that 71% believe they could produce a defensible audit trail for what their AI systems have done. Only 19% actually have the logging, retention, and detection controls to do it. More than half have written policies, which is the easier half.
The watch-for is the distance between those two numbers. A policy states what should happen. Logs are what let you show what did. If AI is touching regulated workflows in your organization, the useful question is not whether a policy exists. It is whether you could reconstruct a decision six months from now, for someone who is not inclined to take your word for it.
Source: Arctera, State of AI Governance 2026, published July 21, 2026.
Stay Tuned for More Peace of Mind
Each issue, we cover the technology decisions that shape how organizations operate and stay resilient. If anything here sparked a question, we would love to hear from you.
Until next time, The Zinfinity Team